Akira Group Leaks 30GB of Data Allegedly Stolen from Pelham Plastics November 11, 2026
Akira ransomware group has listed Pelham Plastics on its data leak site. Pelham Plastics is a custom plastic engineering company that makes injection molds and custom equipment, mainly for medical applications. The listing was posted on November 11, 2026.
What the group claims
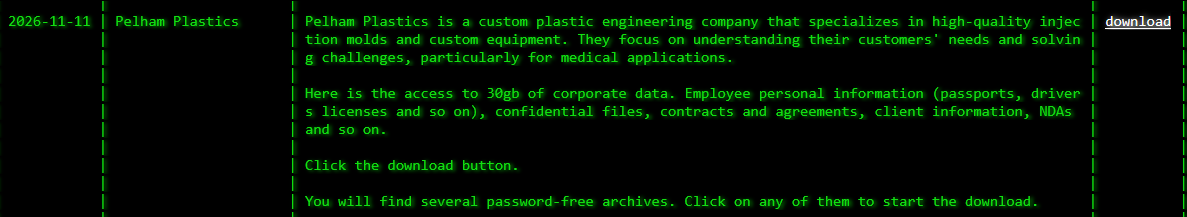
The group says it stole about 30GB of corporate data, including:
- Employee personal information, including passport and driver’s license scans
- Confidential internal files
- Contracts and agreements
- Client information
- Non-disclosure agreements (NDAs)
Data already published
This is not just a threat to leak. The listing includes a download link to several archives with no password, so the data appears to be publicly available already. That usually means ransom negotiations either failed or never started.
Verification status
We have not independently verified the contents of the archives. Pelham Plastics has not made a public statement about the incident at the time of writing.
Potential risks
- Employees: Exposed passport and driver’s license scans create a high risk of identity theft and fraud.
- Clients and partners: The leaked contracts, NDAs, and client information could expose business relationships and confidential project details. Because the company serves the medical sector, this may include proprietary designs for medical devices and their parts.
- Supply chain: Threat actors could use the leaked documents to write convincing phishing or invoice-fraud emails aimed at Pelham Plastics’ clients and suppliers.
Recommendations
- Pelham Plastics’ employees should watch for identity misuse and consider credit monitoring or fraud alerts.
- Clients and partners should be wary of unexpected emails or payment-detail changes that appear to come from Pelham Plastics, and should confirm any such request through a separate channel they already know.
- Manufacturers serving the medical sector should review how they store sensitive client and employee documents, and monitor for large outbound data transfers.
We will update this post as more information becomes available.